
AI works with the information it can access. If connected sources contain sensitive data, exposed credentials, or outdated content, those risks can carry into its answers. As you add more assistants and agents, strong content controls become essential.
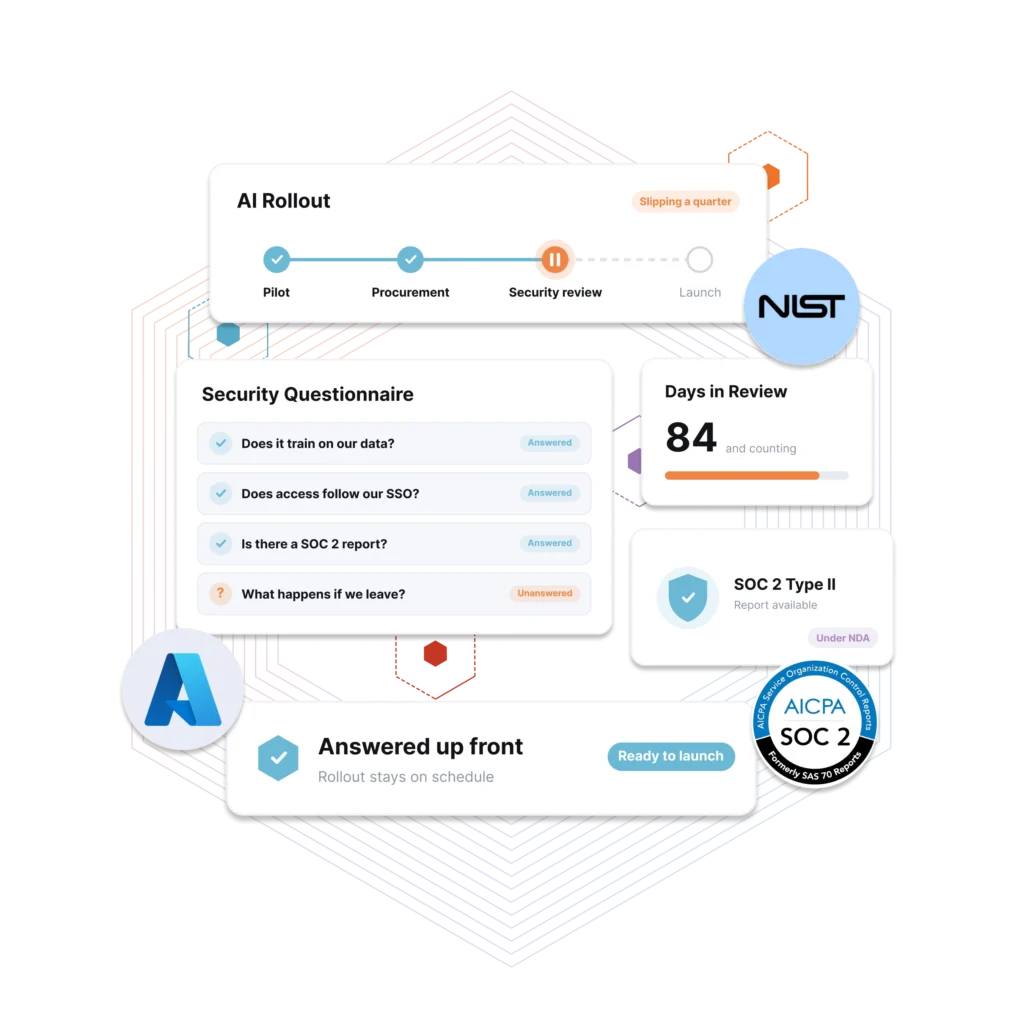
Scale Your AI.
Not Your Risk.
AI tools can access more of your knowledge, including the parts it should never surface. The Enterprise Intelligence Engine™ filters every answer through each user’s permissions before content reaches the model. Your data stays safe and is never used to train models.
Learn How Grounded Reasoning WorksYour AI Inherits the Risks in Your Content

Set the Rules Once and Enforce Them Everywhere AI Works
The Enterprise Intelligence Engine gives every agent the same trusted, secure context, making multi-agent workflows easier to build and scale.
Content Guardrails: Scan posts and connected sources for PII, PHI, GLBA data, and hard-coded credentials. Configurable policies set severity levels and can keep stale or harmful content out of AI retrieval until an admin reviews it.
Permission-Aware Answers: Every request is checked against the user’s community membership and document permissions before any content reaches the model. Access is rechecked every five minutes, so revoked permissions take effect fast.
AI Connect MCP + API: Ground your own agents and assistants in the Enterprise Intelligence Engine, and apply the same reasoning and compliance policies to any AI agent on any model. Every request is recorded in a tamper-evident audit trail.
AI That Makes Your Knowledge More Secure, Not Less

Your Data Stays Yours
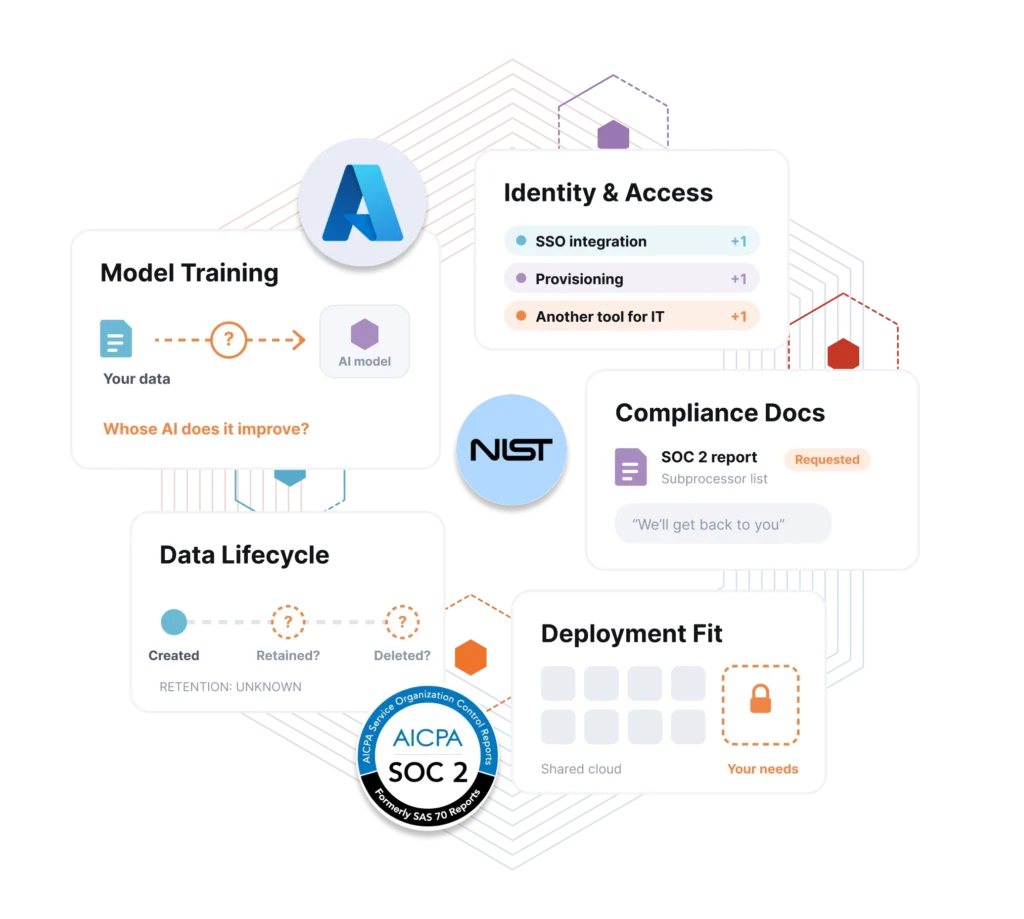
Bloomfire never uses customer content to train or fine-tune its models, and every community’s data stays isolated from every other customer’s. The same guarantee applies whether you’re piloting with 50 users or rolling out to 50,000.

AI That Respects Access
Bloomfire supports SSO and SCIM, including SCIM for Azure Active Directory, so provisioning and deprovisioning follow the identity system your IT team already trusts.

Audit-Ready AI
Bloomfire is SOC 2 Type II compliant and audited annually for security, availability, processing integrity, confidentiality, and privacy. Reports, subprocessor lists, and questionnaire responses are available under NDA.

Governed Content, Trusted Answers
A formal data management policy classifies, retains, and disposes of information on schedule, so AI answers only from governed, current content. The Knowledge Health Report flags compliance risks.
Secure AI in Hours,
Not Weeks
Setting up SSO and SCIM typically takes IT teams under four hours, not the multi-week security project rollout that it usually implies. The rest of the implementation follows the same Plan, Configure, Prepare, Launch process that every Bloomfire customer goes through.
Frequently Asked Questions
Bloomfire encrypts content at rest and in transit, and restricts access to the encryption keys to a small set of authorized engineers. Production systems require unique, authenticated access rather than shared credentials, so no single generic login can reach customer data without a specific, logged reason.
IT setup typically takes under 4 hours, mostly spent connecting SSO and configuring SCIM, including documented support for Azure Active Directory. We handle a vanity URL and firewall allowlist entries in the same pass, so users have a working login on day one.
Yes. Bloomfire is SOC 2 Type II compliant and audited annually for security, availability, processing integrity, confidentiality, and privacy. The full report and subprocessor list are available under NDA through our security team.
Content is classified, retained, and disposed of according to a documented data management policy, not left to sit indefinitely. Migration and off-boarding follow the same policy, so there’s a clear answer for what happens to your content at every stage, not just while you’re an active customer.
That depends on your requirements, and it’s a conversation worth having directly with our security team rather than assuming a standard answer. Most Bloomfire deployments run multi-tenant in the cloud, and enterprise teams with stricter architectural requirements can scope those needs case by case.
It’s built into every phase, not bolted on at the end. Security and IT configuration happen during the Configure phase, before content migration starts, and the Knowledge Health Report audits what’s being brought in before it goes live, so the security review and the rollout happen on the same timeline instead of one blocking the other.
Build your knowledge ecosystem
Connect knowledge pools of documents, conversations, media, data, and expertise with your Persistent Semantic Memory™ to ground your AI. Use our turn-key of connectors or build your own to connect to any enterprise systems.
Sign up for Innovation
The pace of innovation with AI is accelerating. Join an alpha group for early access to new turnkey Intelligence Modules, and help shape what comes next.